In brief
The European Union issued a joint warning over incidents that hit refrigeration systems on 1–2 November 2026. Authorities urged organisations to adopt NIS2 risk‑management measures and respond to the EU Cyber Resilience Act’s reporting and secure‑by‑design requirements. The act will fully enforce secure designs by 11 December 2027, while manufacturers must report severe incidents through the Single Reporting Platform from 11 September 2026.
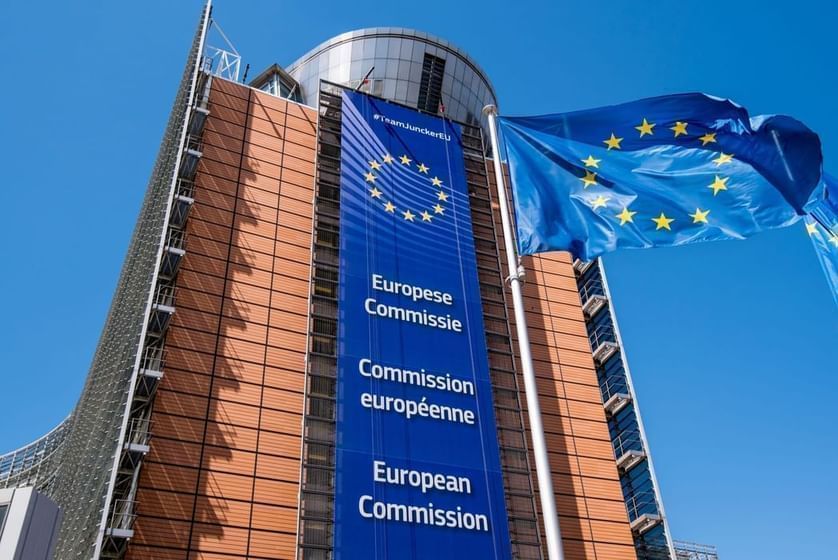
On 5 November 2026, a coalition of European Union cybersecurity agencies—ENISA, the European Commission, Europol’s European Cybercrime Centre, the EU CSIRTs Network, and EU‑CyCLONe—issued a joint warning after a series of incidents that struck refrigeration systems across member states on 1 and 2 November.
The alerts, shared through ENISA’s advisory collection and national cybersecurity response teams, urged private and public organisations to accelerate the implementation of NIS2 risk‑management measures and to tighten the security of their critical refrigeration infrastructure.
Background
Refrigeration systems are essential to food safety, pharmaceutical storage and several industrial processes. Recent cyberattacks demonstrated that a compromised cold‑chain can compromise public health and economic stability. In response, the European Union’s cybersecurity community coordinated the investigation and information‑sharing efforts across national teams and crisis‑management authorities.
Authorities noted that the recent wave of attacks occurred in the first two days of November, prompting an urgent response. While member states are still analysing the technical details, the joint warning underscores the urgency of mitigation and prevention.
Regulatory Framework
Under the EU Cyber Resilience Act, which entered force for reporting on 11 September 2026, manufacturers of digital COBOTs, including refrigeration units, must notify the EU’s Single Reporting Platform about severe incidents and actively exploited vulnerabilities. The Act also introduces secure‑by‑design and secure‑by‑default principles, demanding that manufacturers embed security into product design, provide continuous support throughout the product life cycle, and remediate vulnerabilities without delay. The main security requirements of the Act will become fully enforceable by 11 December 2027.
Enforcement is complemented by the NIS2 Directive, which obliges covered organisations to adopt risk‑management measures, conduct regular security assessments, and report significant incidents to national authorities or computer security incident‑response teams. The joint warning stresses that failure to comply could result in penalties and increased exposure to further cyber threats.
According to ENISA, the advisory collection continues to promote secure‑by‑design principles and encourages the exchange of technical information and best practices. ENISA emphasized that organisations should directly consult the latest security advisories issued by national cybersecurity authorities and the EU CSIRTs Network, as well as the EU‑CyCLONe’s situational reports.
Organisations affected by the cooling‑system breaches are advised to implement multilayered defenses: secure firmware updates, hardened intrusion detection systems, and continuous monitoring of system logs. Manufacturers are also prompted to publish detailed vulnerability‑management timelines and to engage with certification bodies to validate compliance.
Member states are coordinating the emergency response to protect critical infrastructure, while the EU agencies monitor the situation to ensure a cohesive and rapid counter‑measure deployment across the bloc.